Latest Cybersecurity News and Articles
Critical Flaw in LayerSlider WordPress Plugin Impacts One Million Sites
05 April 2024
A premium WordPress plugin named LayerSlider, used in over one million sites, is vulnerable to unauthenticated SQL injection, requiring admins to prioritize applying security updates for the plugin.
Researchers Identify Multiple China Hacker Groups Exploiting Ivanti Security Flaws
05 April 2024
Multiple China-nexus threat actors have been linked to the zero-day exploitation of three security flaws impacting Ivanti appliances (CVE-2023-46805, CVE-2024-21887, and CVE-2024-21893).
The clusters are being tracked by Mandiant under the monikers UNC5221, UNC5266, UNC5291, UNC5325, UNC5330, and UNC5337. Another group linked to the exploitation spree is UNC3886.
The Google Cloud
Senior Tory ‘mortified’ after reportedly passing MPs’ data to dating app contact
04 April 2024
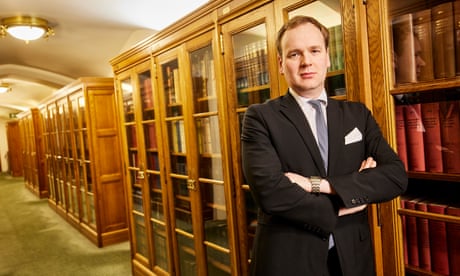 William Wragg says he was pressed for colleagues’ details after sharing compromising photos of himselfA senior Conservative MP has reportedly admitted to giving out the personal phone numbers of colleagues to a person he met on a dating app.William Wragg told the Times that he gave the information after he had sent intimate pictures of himself, saying he was “scared” and “mortified”. Continue reading...
Police launch inquiry after MPs targeted in apparent ‘spear-phishing’ attack
04 April 2024
 At least a dozen people sent suspicious messages, with senior figures suggesting foreign state could be culpritA police investigation has been launched after MPs were apparently targeted in a “spear-phishing” attack, in what security experts believe could be an attempt to compromise parliament.A police force said it had started an inquiry after receiving a complaint from an MP who was sent a number of unsolicited messages last month. Continue reading...
DHS proposes reporting rules for critical infrastructure
04 April 2024
Security leaders respond to the proposed critical infrastructure rules set forth by the DHS.
Vietnam-Based Hackers Steal Financial Data Across Asia with Malware
04 April 2024
A suspected Vietnamese-origin threat actor has been observed targeting victims in several Asian and Southeast Asian countries with malware designed to harvest valuable data since at least May 2023.
Cisco Talos is tracking the cluster under the name CoralRaider, describing it as financially motivated. Targets of the campaign include India, China, South Korea, Bangladesh, Pakistan, Indonesia,
New Phishing Campaign Targets Oil & Gas with Evolved Data-Stealing Malware
04 April 2024
An updated version of an information-stealing malware called Rhadamanthys is being used in phishing campaigns targeting the oil and gas sector.
"The phishing emails use a unique vehicle incident lure and, in later stages of the infection chain, spoof the Federal Bureau of Transportation in a PDF that mentions a significant fine for the incident," Cofense researcher Dylan Duncan said.
The
Scrut Automation Secures $10 Million in Growth Capital
04 April 2024
Scrut Automation, a GRC platform provider, has announced today that it secured $10 million in growth capital from its existing investors, including Lightspeed, MassMutual Ventures, and Endiya Partners.
Fake Lawsuit Threat Exposes Privnote Phishing Sites
04 April 2024
A cybercrook who has been setting up websites that mimic the self-destructing message service Privnote.com accidentally exposed the breadth of their operations recently when they threatened to sue a software company. The disclosure revealed a profitable network of phishing sites that behave and look like the real Privnote, except that any messages containing cryptocurrency addresses will be automatically altered to include a different payment address controlled by the scammers.
New SEXi Ransomware Gang Targets VMware ESXi Servers
04 April 2024
Chilean data center and hosting provider IxMetro Powerhost has suffered a cyberattack at the hands of a new ransomware gang known as SEXi, which encrypted the company's VMware ESXi servers and backups.
Targeted Phishing Linked to 'The Com' Surges in the US, the UK, and Canada
04 April 2024
A persistent social engineering threat faced by enterprises involves attackers trying to obtain login credentials for identity and access management (IAM), cloud resources, or single sign-on (SSO)-enabled systems.
Report: 73% Brace for Cybersecurity Impact on Business in the Next Year or Two
04 April 2024
Only 3% of organizations across the globe have the ‘mature’ level of readiness needed to be resilient against modern cybersecurity risks, according to Cisco. The readiness is down from one year ago, when 15% of companies were ranked mature.
Microsoft Exchange State-Linked Hack Entirely Preventable, Cyber Review Board Finds
04 April 2024
The China-affiliated threat actor Microsoft identified as Storm-0558 compromised the Microsoft Exchange Online mailboxes of 22 organizations and more than 500 individuals in the attacks, which began in May 2023.
Distinctive Campaign Evolution of Pikabot Malware
04 April 2024
PikaBot, along with other malicious loaders like QBot and DarkGate, heavily depends on spam campaigns for distribution. Its initial access strategies are intricately crafted, utilizing geographically targeted spam emails for specific countries.
Considerations for Operational Technology Cybersecurity
04 April 2024
Operational Technology (OT) refers to the hardware and software used to change, monitor, or control the enterprise's physical devices, processes, and events. Unlike traditional Information Technology (IT) systems, OT systems directly impact the physical world. This unique characteristic of OT brings additional cybersecurity considerations not typically present in conventional IT security
New HTTP/2 Vulnerability Exposes Web Servers to DoS Attacks
04 April 2024
New research has found that the CONTINUATION frame in the HTTP/2 protocol can be exploited to conduct denial-of-service (DoS) attacks.
The technique has been codenamed HTTP/2 CONTINUATION Flood by security researcher Bartek Nowotarski, who reported the issue to the CERT Coordination Center (CERT/CC) on January 25, 2024.
"Many HTTP/2 implementations do not properly limit or sanitize the
Magento Shoplift Malware Targets Both WordPress and Magento CMS on E-Commerce Sites
04 April 2024
While it pretends to be a Google Analytics script, this is merely a distraction from the true nature of the credit card skimming JavaScript code snippet embedded in the infected website.
Unveiling the Fallout: Operation Cronos' Impact on LockBit Following Landmark Disruption
04 April 2024
Contrary to what the group themselves have stated, activities observed post-disruption would indicate that Operation Chronos has a significant impact on the group’s activities.
Google Fixed Another Chrome Zero-Day Exploited at Pwn2Own
04 April 2024
The vulnerability CVE-2024-3159 is an out-of-bounds memory access in the V8 JavaScript engine. The flaw was demonstrated by Edouard Bochin (@le_douds) and Tao Yan (@Ga1ois) of Palo Alto Networks during the Pwn2Own 2024 on March 22, 2024.
Rhadamanthys Stealer Delivered in Transportation Campaign
04 April 2024
The phishing emails use a unique vehicle incident lure and, in later stages of the infection chain, spoof the Federal Bureau of Transportation in a PDF that mentions a significant fine for the incident.